included ldap login support for webadmin - #49
twinfield (tylerwinfield) wants to merge 7 commits into
Conversation



added installation of php ldap module to required software installs
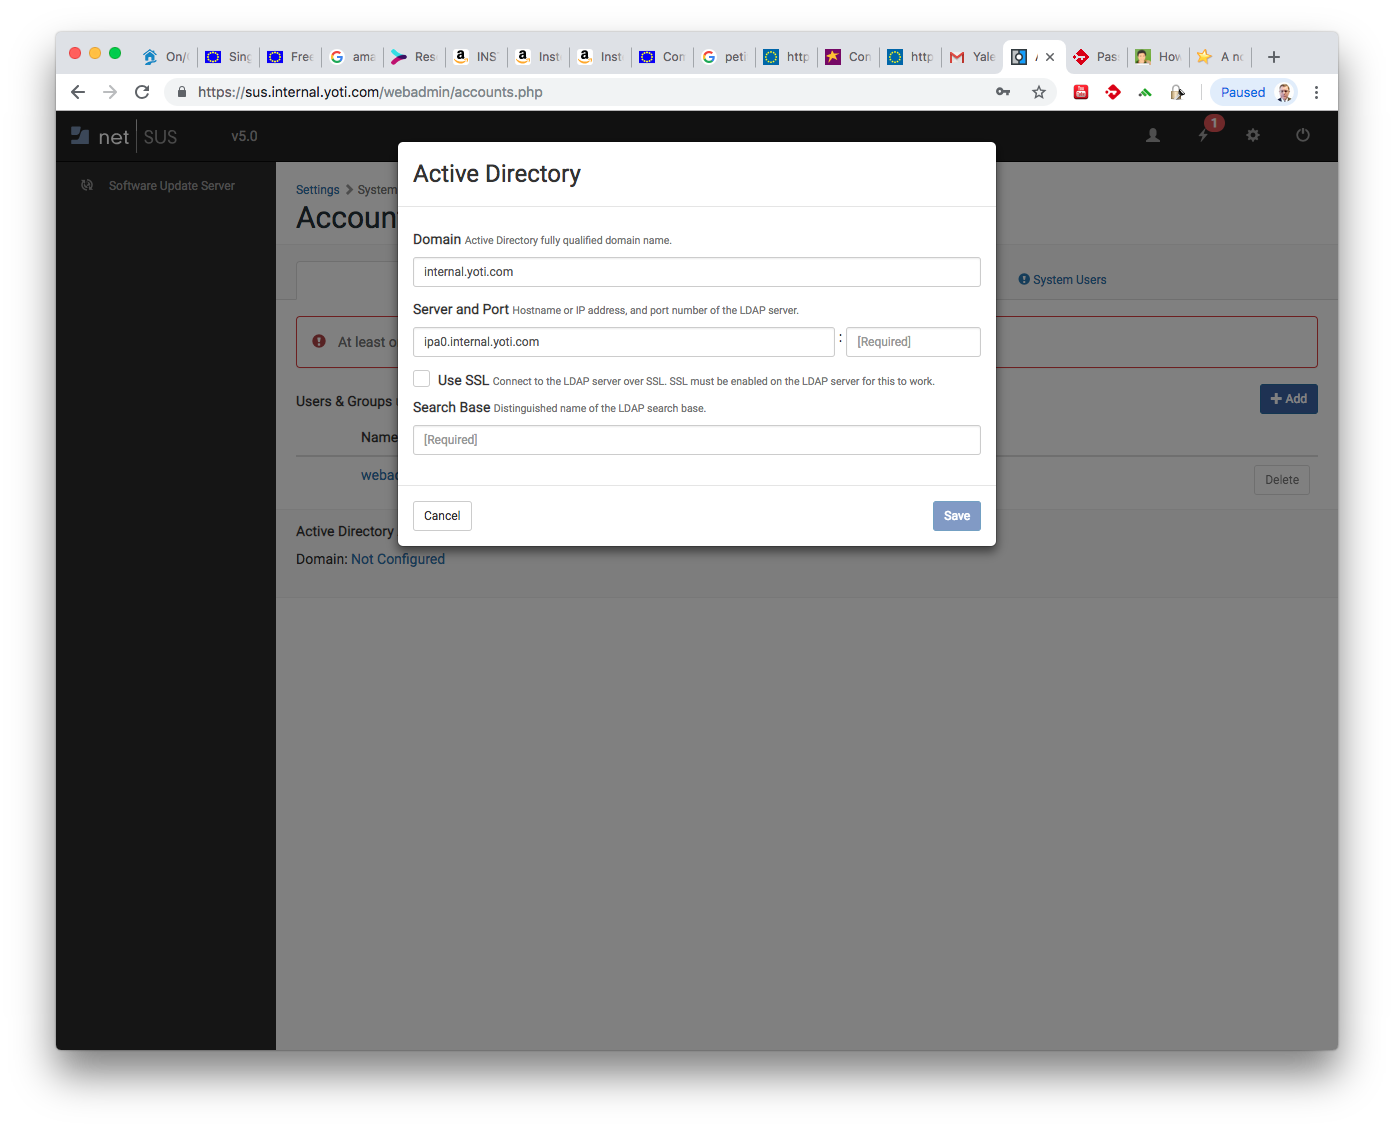
included login support for ldap accounts
created ldap configuration page under webadmin settings
included support to purge all deprecated updates from SUS
added button for update purge to webadmin
This reverts commit afae439.
included functions for purging of deprecated updates
added button to webadmin for purge function
store username as session variable
display function returns session username first if it is set

|
Hi, 👍 Is there any plans on merging this ? With ChrOst@ff6dc03 for Active Directory login, it would be awesome! Thanks! |

|
Nicolas Brechet (@nicolasbrechet) Jamf (@jamf) It seems that ChrOst (@ChrOst) has made the changes requested by Jamf (@jamf) here: #14 (comment) Thoughts on a merge? Would be wonderful. |

extra "=" symbol crashing PHP


|
There are currently some merge conflicts but upon resolution of these conflicts we will merge. |

|
Why not verify the user against the JSS API? Then you would not have to re-enter all the LDAP information? |

|
Christoph von Gabler-Sahm (@cvgs) and what do you find a valid login if you run multiple sites with different AdminGroups? |
|
ChrOst (@ChrOst) You would have to not only check the login credentials, but also evaluate the user’s granular permissions and then "hijack" an existing permission for indirect verification. |
|
This has been implemented with the new UI. |


|
Steven Strand (@StevenStrand) What am I missing? I am running NetSUS 5.0 on Ubuntu 16.04.
|
7 participants


updated installation script to install ldap module for php
added support for ldap logins to webadmin
redesigned lookup process to improve security